
CSS frameworks · Framework 07 of 08
The Never List
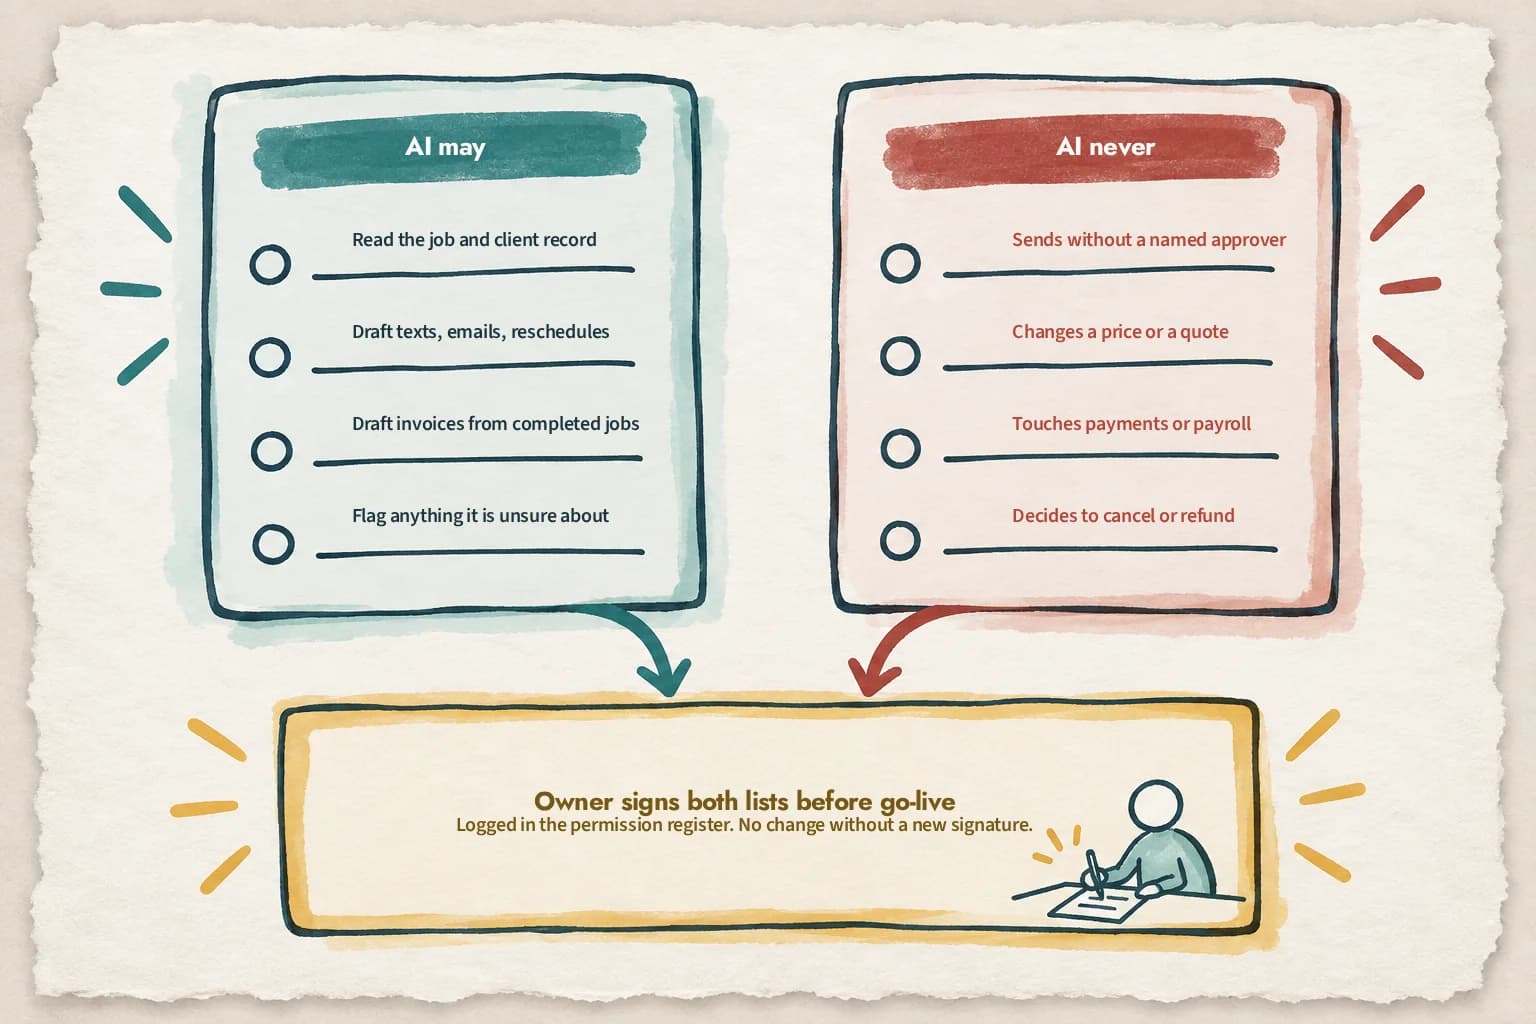
Before anything goes live, you sign the list of what AI never sends, never decides and never touches. The permission register is its ledger.
Why it matters
The question every owner asks is "what could it do that I'd regret?" The answer should be a document, not a reassurance.
A written Never List turns a vague fear into a boundary you set yourself: no price changes, no refunds, no payroll, nothing sent without a named approver.
It also protects your team, who can act freely inside the line because the line is clear.
How we apply it
- In month 1 of AI Implementation we draft two lists side by side: what each AI employee may read and draft, and what it never does.
- You edit both and sign. The signed version goes in the permission register with a date.
- Every connector and permission we add after that is logged against the list, with who approved it.
- Quarterly we review the register with you and report any drift between what's allowed on paper and what's connected in practice.
The number
| Measure | Cadence | Baseline |
|---|---|---|
| Permission changes, each with its approver | Monthly | Signed list, month 1 |
| Drift found between register and live connections | Quarterly | Target zero |
| AI employees with a named approver | Monthly | All of them |
Who is accountable
No change to the list without your sign-off, ever, including changes that would make our work easier.
If we connect something the register doesn't cover, that is our breach, reported to you the day we find it.
Where you meet it
AI Implementation, month 1; the Team AI Starter Kit has the DIY template.
A common question
The Never List, asked and answered.
Can the list change later?
Yes, with your signature. Most clients loosen it after a few months of clean approval data, and the register shows exactly when and why.